

NETWORKING DINNER | NEW YORK
ABOUT THIS EVENT
Most cyberattacks touch DNS at some point, whether attackers are establishing command-and-control (C2) channels, exfiltrating data via tunneling, or rotating through newly registered domains (NRDs) and encrypted protocols (DoH/DoT) to evade perimeter controls. In hybrid cloud environments, DNS traffic often falls into an operational blind spot between networking and security teams, leaving no single owner to inspect it end-to-end.
This roundtable brought together network security leaders from financial services and insurance firms in New York to compare strategies for securing DNS across on-premises infrastructure and AWS environments.
Key Discussion Topics:
WHY ATTEND
Common Sense Events uses a conversational, story-telling approach designed for peer learning. Every participant’s voice shapes the discussion – no slides, no pitch decks.
This was an executive peer group meet for 10 – 12 senior leaders. Participation in this in-person networking session was at no cost for qualified attendees.
AGENDA
6:00 PM
Arrival, Drinks and Networking
6:30 PM
Welcome and Introductions
6:45 PM
Roundtable Discussion and Dinner
8:45 PM
Closing
VENUE
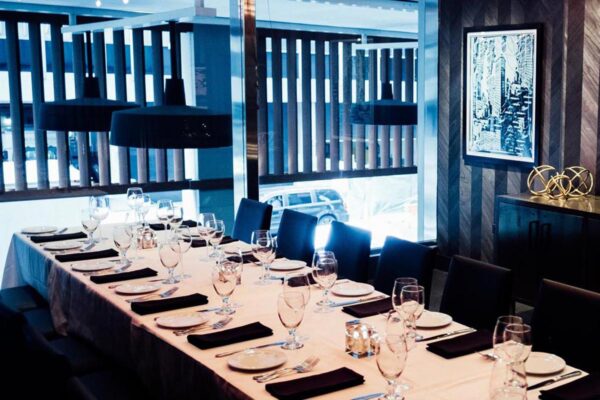
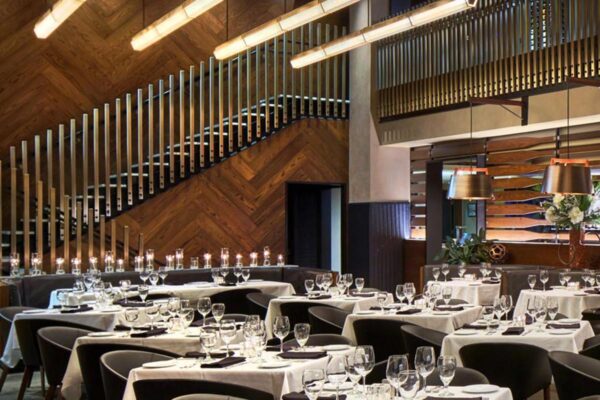
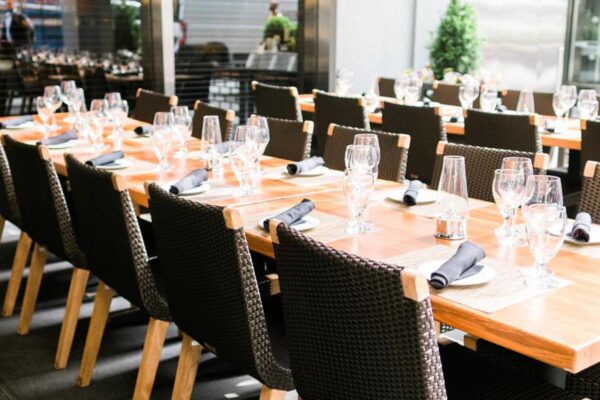
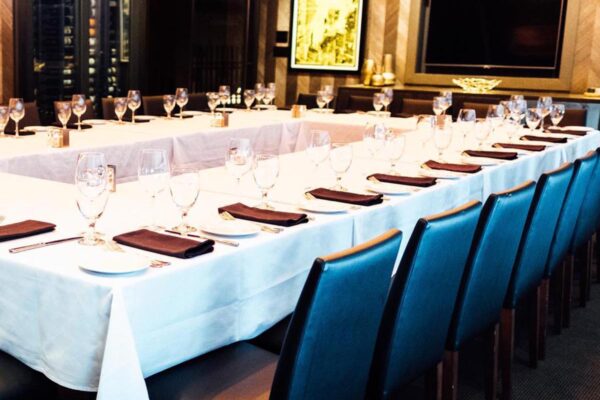
Ocean Prime, New York
123 W 52nd St, New York, NY 10019,
United States
REGISTRATION
Event concluded
No cost for qualified attendees. Once you’ve applied, we’ll review your submission and confirm your invitation with a calendar invite and venue directions.
Questions? Contact our representative:
+1 218-302-1460
[email protected]