Sizing Your Quantum Exposure Before You Migrate
AWS has already moved TLS connections to services such as KMS, ACM and Secrets Manager to hybrid post-quantum key exchange. That covers the cloud provider’s side. Your applications, VPN tunnels, private PKI, code signing and long-lived signatures stay your responsibility, and so does the vendor software running inside them.
The regulatory clock is also moving.
CNSA 2.0 requires quantum-safe algorithms for new US national security system purchases from January 2027, EU member states must submit national PQC plans by the end of 2026, and the UK NCSC expects organizations to finish discovery and planning by 2028. Regulated enterprises outside those mandates are seeing the same dates show up in auditor questions and customer due diligence.
Most migration plans stall at the first step: nobody has a complete picture of where RSA and elliptic curve cryptography sit across cloud workloads, on-premises systems and third parties. Without that picture, sequencing and budgets are estimates.
Join Scott Francis, Principal Director at Accenture Security, alongside AWS and a small group of security and technology leaders to compare how you are scoping exposure, setting timelines and deciding what to automate.
Principal Director
at Accenture Security
DISCUSSION TOPICS
AGENDA
5:30 PM
Arrival, Welcome and Introductions
5:45 PM
Roundtable Discussion
6:30 PM
Networking Dinner
8:00 PM
Closing
REGISTRATION
No cost for qualified attendees. Once you’ve applied, we’ll review your submission and confirm your invitation with a calendar invite.
Attendance is by invitation only.
VENUE
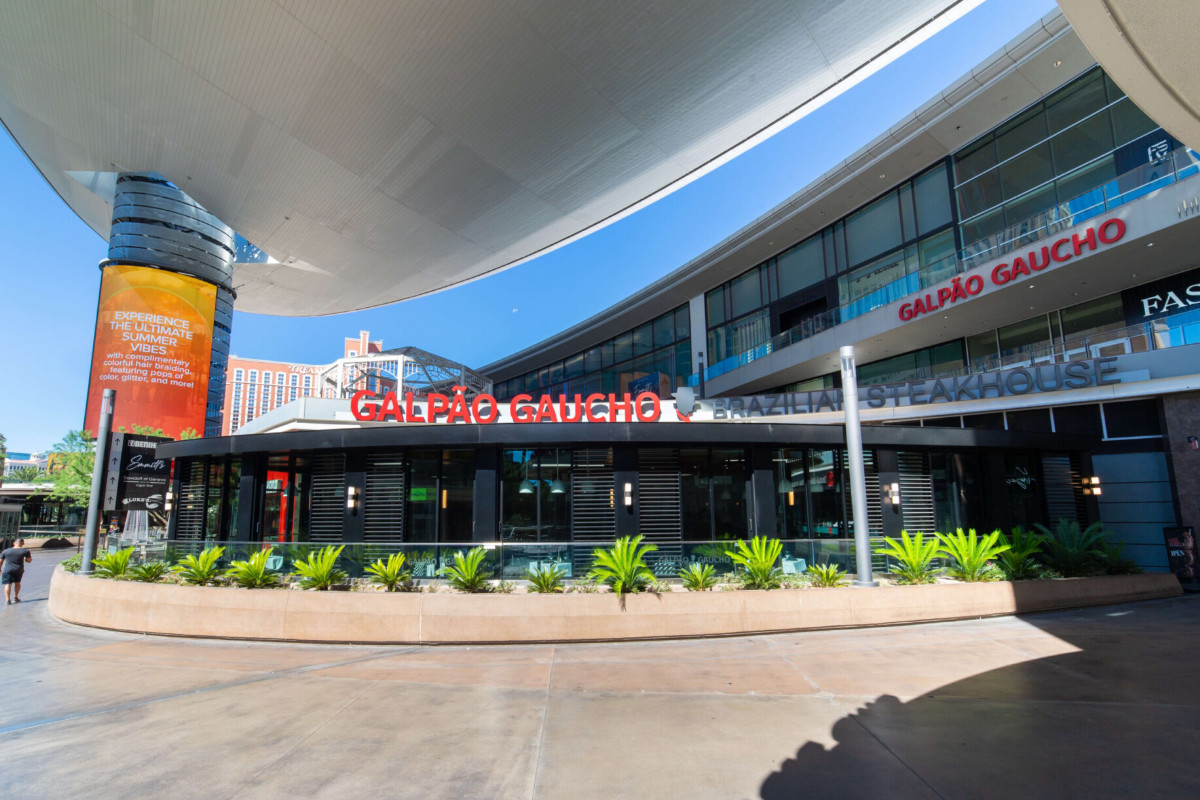
Galpão Gaucho Brazilian Steakhouse, Las Vegas
3200 S Las Vegas Blvd, Suite 1260, Las Vegas, NV 89109